
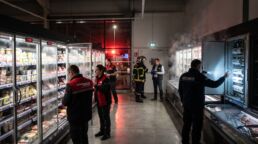
Unprecedented Cyber-Physical Attack Hits French Supermarkets, Triggering Fire Hazards and Food Spoilage
Paris, France — The line between digital threats and physical destruction has been dramatically blurred following an unprecedented cyberattack on the Intermarché supermarket chain in France. Between the night of October 11 and October 12, malicious hackers infiltrated the Operational Technology (OT) networks governing the refrigeration and climate control systems of over 150 store locations. The attack not only resulted in the massive spoilage of perishable food items but also induced critical hardware malfunctions that led to localized fire hazards, prompting an immediate national investigation.
The Intermarché incident represents a terrifying evolution in cyber warfare and criminal extortion: the cyber-physical attack. Unlike traditional IT breaches that target data confidentiality or digital operations, cyber-physical attacks manipulate internet-connected hardware to cause tangible, real-world damage. In this case, the attackers compromised the central IoT (Internet of Things) management platforms used by the supermarket chain to monitor and regulate store temperatures.
Once inside the network, the threat actors systematically deactivated the cooling mechanisms in industrial freezers and refrigerators across 150 locations. As temperatures rose, millions of euros worth of meat, dairy, and frozen goods were rendered unsafe for consumption, dealing a massive financial blow to the retail chain and disrupting local food supply networks. However, the attackers did not stop at simply turning the systems off. In a highly alarming escalation, they manipulated the operational parameters of the refrigeration compressors, pushing the machinery beyond safe limits.
This deliberate overexertion caused the hardware to severely overheat, triggering smoke alarms and minor electrical fires in several stores. The physical danger posed to employees and customers forced emergency evacuations and the deployment of local fire departments. The French government has treated the incident as a matter of national security, with the national cybersecurity agency (ANSSI) launching a full-scale investigation into how the vulnerability was exploited and identifying the perpetrators behind this reckless act of sabotage.
The vulnerability of OT and IoT systems is a well-documented but persistently unaddressed issue in many non-industrial sectors. Retailers, hospitals, and commercial real estate heavily rely on smart building management systems to improve efficiency. However, these systems are frequently integrated into broader corporate networks without adequate segmentation. If a hacker breaches a standard IT network via a phishing email, a lack of segmentation allows them to pivot seamlessly into the OT environment where the physical hardware is controlled.
Security researchers note that this attack should serve as a wake-up call for the retail industry and beyond. Securing these environments requires specialized approaches, including strict network micro-segmentation, continuous anomaly detection tailored for industrial protocols, and manual hardware overrides that cannot be bypassed via software commands. The Intermarché crisis is a chilling demonstration that as our physical infrastructure becomes increasingly digitized, the consequences of poor cybersecurity can quickly escalate from financial loss to physical catastrophe.